
The Portuguese giant EDP group suffered a ransomware attack at the beginning of April 2020. Crooks are now sharing sensitive data from the organization since the Portuguese electricity giant has not paid the ransom of 10 million euros.
According to the publication of the group that operates the Ragnar_Locker ransomware, two new files were added to the PoC already published on the server on the dark web on April 6th (7 days before the official date of the cyber attack).
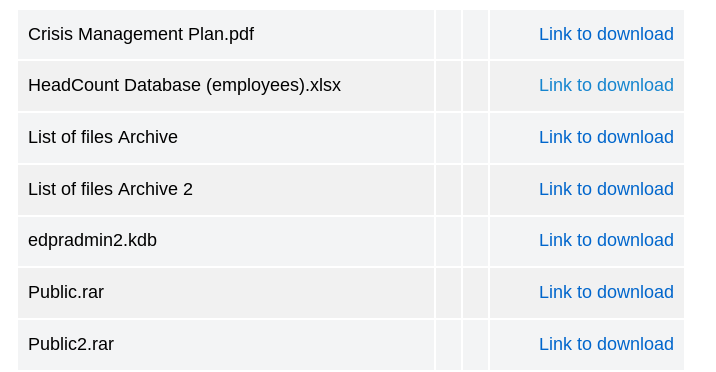
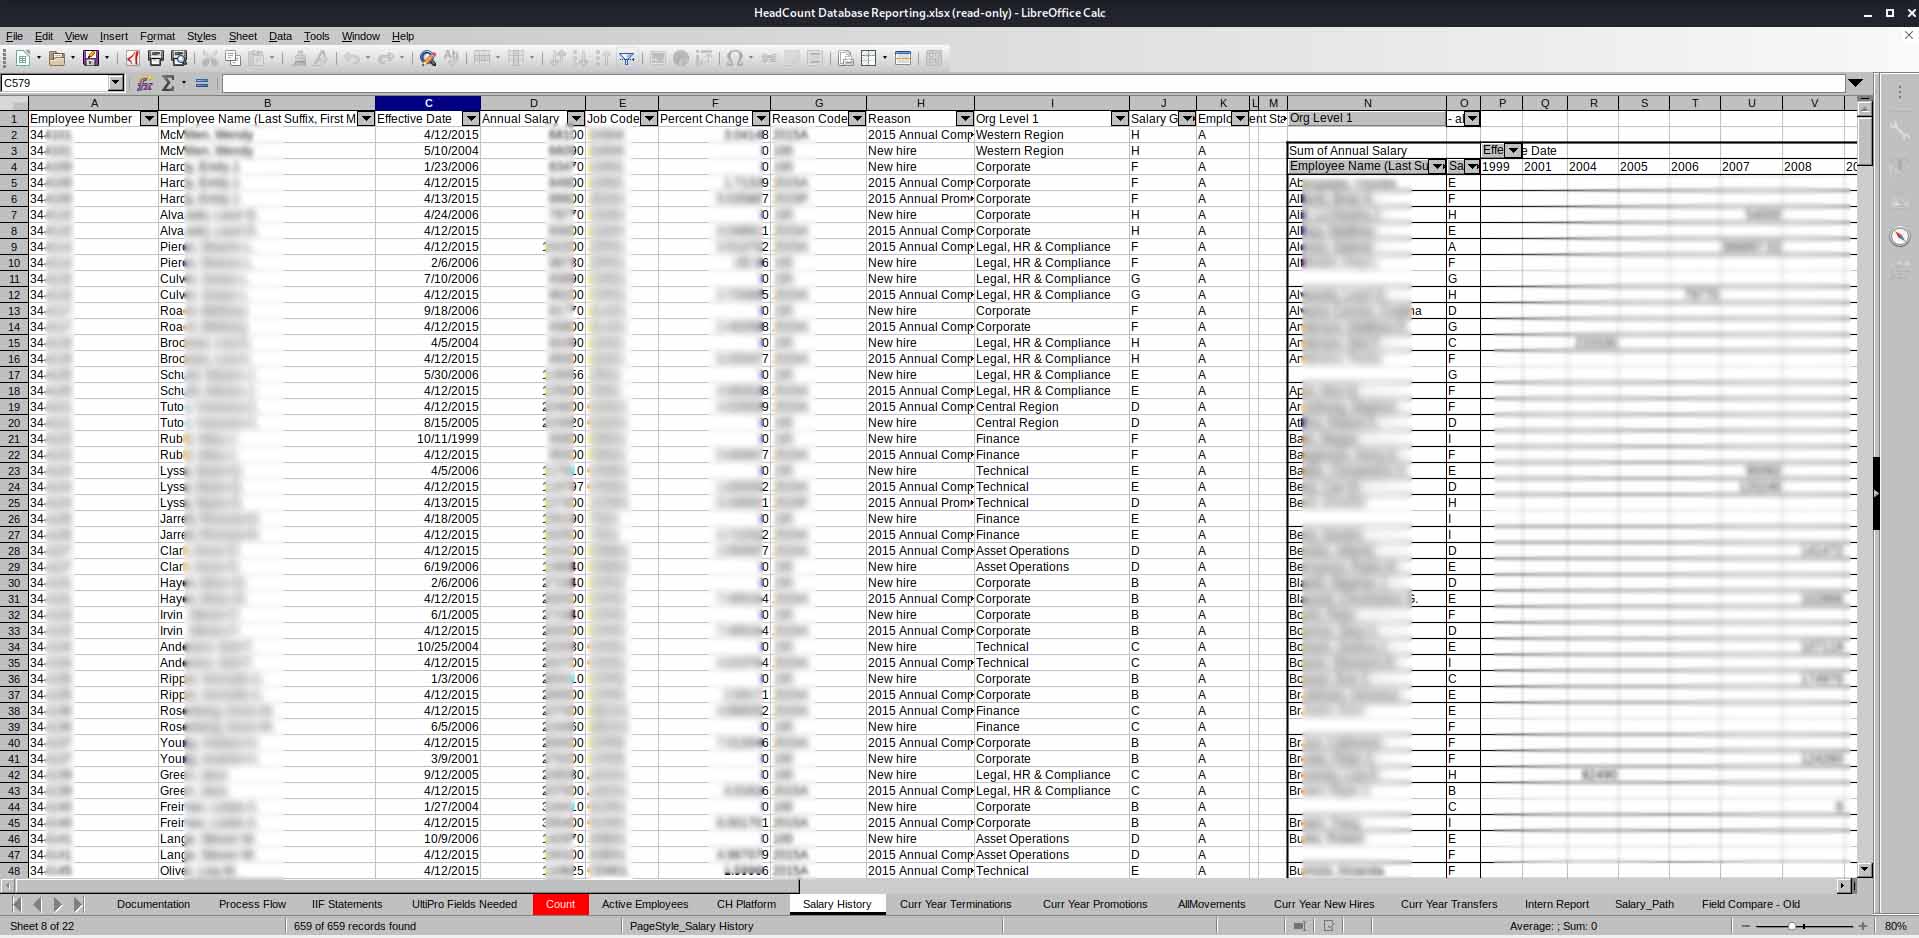
In this recent publication, the new files leak information from a list of employees of the organization in the USA, with the ordered list of workers, salary history between 1999 and 2015, worker promotions, etc.
The other document released is a crisis management plan from EDP Group.
 |
 |

Pedro Tavares is a professional in the field of information security working as an Ethical Hacker/Pentester, Malware Researcher and also a Security Evangelist. He is also a founding member at CSIRT.UBI and Editor-in-Chief of the security computer blog seguranca-informatica.pt.
In recent years he has invested in the field of information security, exploring and analyzing a wide range of topics, such as pentesting (Kali Linux), malware, exploitation, hacking, IoT and security in Active Directory networks. He is also Freelance Writer (Infosec. Resources Institute and Cyber Defense Magazine) and developer of the 0xSI_f33d – a feed that compiles phishing and malware campaigns targeting Portuguese citizens.
Read more here.