
This week a huge set of information on the Islamic state has been shared in a Dark Web forum.
The first occurrence of this share was registered in a tweet by @GhostSquadHack published on February 13th.

All data have been extracted from the victim’s mobile devices, including, satellite geo-location, target’s Telegram images folder (sdcard) and target’s WhatsApp images folder (sdcard). Phone numbers, documents, credit cards, identification cards/documents, Telegram, Facebook and Twitter accounts as well as IP logs were also exfiltrated by crooks.

As shown, data from several countries were found in this collection, including Indonesia, Morocco, Turkey, India, etc.
Many personal photographs, videos, SMS, phone numbers extracted from the hacked devices can be found by analyzing the data, as well as images and documents of the group’s internal publications.
Additional evidence is presented below.
(medicare card)
 (contact list sample)

(SMSs)

(Telegram account and details)
(Telegram account details 2)
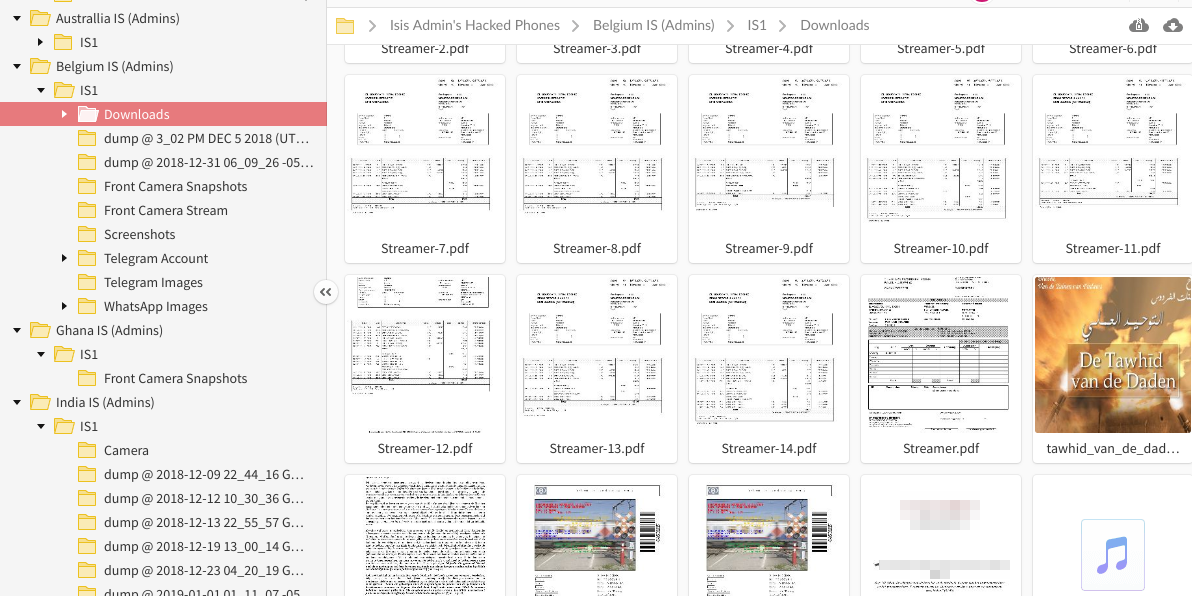
(other documents)
According to this share, Telegram and WhatsApp are the preferred communication channel used by members of the Islamic state.
The leak is now available for download and can be used for malicious purposes.
No more information is available at the moment.

Pedro Tavares is a professional in the field of information security working as an Ethical Hacker/Pentester, Malware Researcher and also a Security Evangelist. He is also a founding member at CSIRT.UBI and Editor-in-Chief of the security computer blog seguranca-informatica.pt.
In recent years he has invested in the field of information security, exploring and analyzing a wide range of topics, such as pentesting (Kali Linux), malware, exploitation, hacking, IoT and security in Active Directory networks. He is also Freelance Writer (Infosec. Resources Institute and Cyber Defense Magazine) and developer of the 0xSI_f33d – a feed that compiles phishing and malware campaigns targeting Portuguese citizens.
Read more here.